CROSS-INTEL Ransomware Alert 🇺🇸
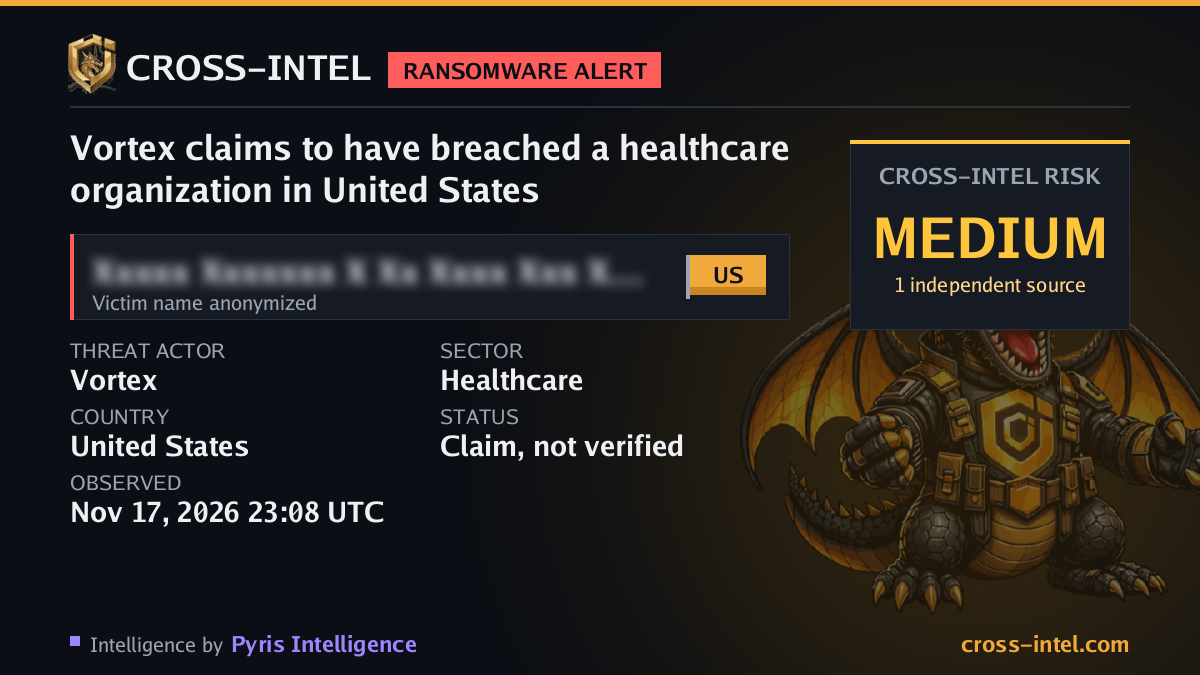
VORTEX claims to have breached a healthcare organization in United States (D**** M****** - 1, 4**, 8** r******).
Threat actor: Vortex
Sector: Healthcare
Country: United States
Data claimed: not specified
Observed: Nov 17, 2026 23:08 UTC
Status: Claim, not verified
CROSS-INTEL Risk: Medium (1 independent source)
Threat actor: Vortex
- Victims listed, last 30 days: 35
- Victims listed, last 12 months: 35
- Latest listing: Nov 18, 2026
- Sectors targeted: Healthcare (12), Manufacturing (3), Financial services (1), Professional Services (1)
- Countries targeted: United States (16), Germany (1)
- CROSS-INTEL alerts about it: 1
About this alert
CROSS-INTEL detects these events from what Pyris Intelligence collects worldwide: ransomware and extortion leak sites as public trackers report them, hacktivist claims, the Known Exploited Vulnerabilities catalog and spikes across independent sources. A victim is named in an anonymized form, and a claim is the group's own: it is not verified. CROSS-INTEL never links to a criminal site.
Monitor your company's exposure
See what the criminal underground already holds about your organization, and get alerted when it changes.