CROSS-INTEL Ransomware Alert 🇺🇸
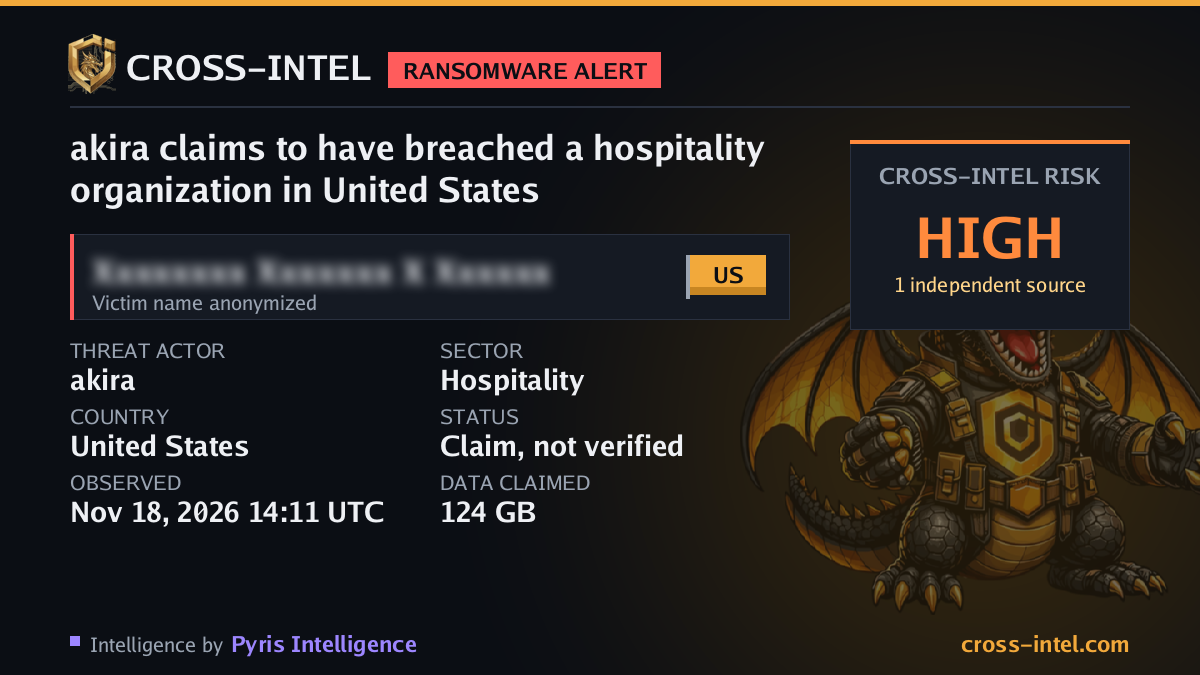
AKIRA claims to have breached a hospitality organization in United States (F******* C****** & E*****).
Threat actor: akira
Sector: Hospitality
Country: United States
Data claimed: 124 GB
Observed: Nov 18, 2026 14:11 UTC
Status: Claim, not verified
CROSS-INTEL Risk: High (1 independent source)
Threat actor: akira
- Aliases: GOLD SAHARA, Howling Scorpius, PUNK SPIDER
- Victims listed, last 30 days: 42
- Victims listed, last 12 months: 63
- Latest listing: Nov 18, 2026
- Sectors targeted: Manufacturing (14), Professional Services (6), Retail & E-Commerce (5), Technology (4)
- Countries targeted: United States (13), Canada (3), Germany (2), Switzerland (1), France (1)
- Techniques (MITRE ATT&CK): T1018 Remote System Discovery, T1021.001 Remote Desktop Protocol, T1027.001 Binary Padding, T1036.005 Match Legitimate Resource Name or Location, T1059.001 PowerShell, T1078 Valid Accounts, T1133 External Remote Services, T1213.002 Sharepoint, T1219 Remote Access Tools, T1482 Domain Trust Discovery, T1486 Data Encrypted for Impact, T1531 Account Access Removal, and 5 more
- CROSS-INTEL alerts about it: 2
About this alert
CROSS-INTEL detects these events from what Pyris Intelligence collects worldwide: ransomware and extortion leak sites as public trackers report them, hacktivist claims, the Known Exploited Vulnerabilities catalog and spikes across independent sources. A victim is named in an anonymized form, and a claim is the group's own: it is not verified. CROSS-INTEL never links to a criminal site.
Monitor your company's exposure
See what the criminal underground already holds about your organization, and get alerted when it changes.